Critical NPM Security Alert: 18 Core Packages Compromised
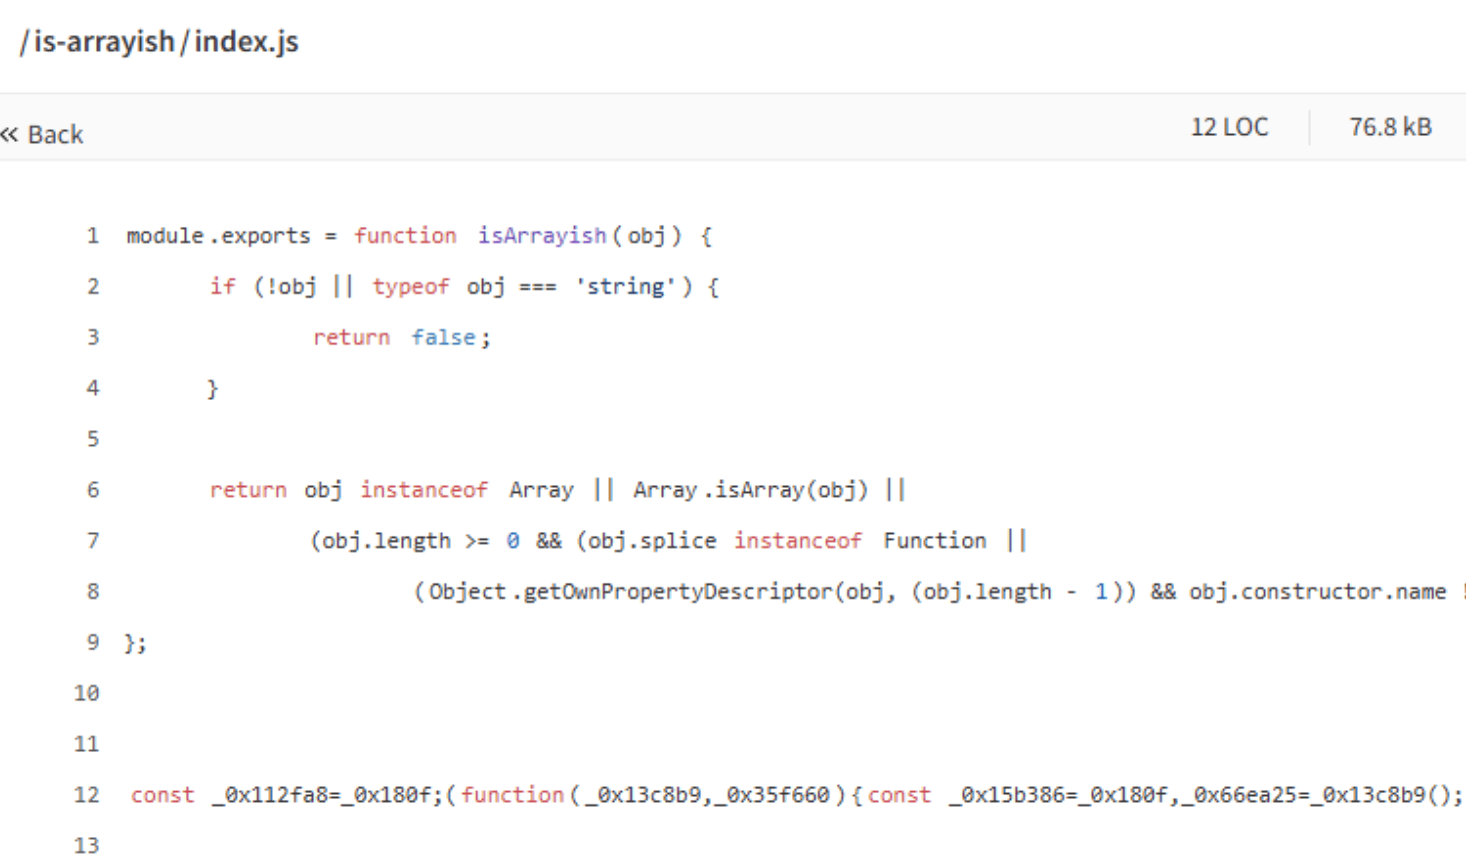
URGENT: On September 8, 2025, 18 essential npm packages with 2+ billion weekly downloads were compromised with malicious code. Immediate action required.
Quick Detection Commands
Check Your System Now (30 seconds)
NPM Users – Run this immediately:
npm ls --depth=100 | grep -E 'debug@4.4.2|chalk@5.6.1|ansi-styles@6.2.2|strip-ansi@7.1.1|color-convert@3.1.1|wrap-ansi@9.0.1' || echo "✅ System Clean"Yarn Users:
yarn list --pattern '' | grep -E 'debug@4.4.2|chalk@5.6.1|ansi-styles@6.2.2' || echo "✅ System Clean"Compromised Packages
| Package | Malicious Version | Weekly Downloads | Risk Level |
|---|---|---|---|
| debug | 4.4.2 | 357.6M | CRITICAL |
| chalk | 5.6.1 | 299.99M | CRITICAL |
| ansi-styles | 6.2.2 | 371.41M | CRITICAL |
| strip-ansi | 7.1.1 | 261.17M | CRITICAL |
| color-convert | 3.1.1 | 193.5M | CRITICAL |
| + 13 additional packages |
Immediate Response Plan
Step 1: Remove Compromised Packages
#!/bin/bash
# Clear npm cache
npm cache clean --force

# Remove malicious packages
npm uninstall debug chalk ansi-styles strip-ansi color-convert wrap-ansi

# Delete node_modules and lock files
rm -rf node_modules package-lock.json
Step 2: Install Safe Versions
// Add to package.json
"overrides": {
  "debug": "4.3.4",
  "chalk": "4.1.2",
  "ansi-styles": "4.3.0",
  "strip-ansi": "6.0.1",
  "color-convert": "2.0.1"
}
# Reinstall dependencies
npm install
npm auditAWS Automated Response
SSM Document for EC2 Scanning
For AWS users, we’ve created an automated scanning solution using Systems Manager:
- Create SSM Document: Deploy our scanning document to automatically check all EC2 instances
- Run Command: Execute across your entire fleet with one command
- Auto-tagging: Infected instances are automatically tagged for isolation
- Reporting: Results uploaded to S3 with SNS notifications
# Execute scanning across all environments
aws ssm send-command \
  --document-name "NPM-Security-Scanner" \
  --targets "Key=tag:Environment,Values=Production,Staging,Development" \
  --parameters '{"S3BucketName":"security-audits"}'

# Check infected instances
aws ec2 describe-instances \
  --filters "Name=tag:npm-scan-status,Values=INFECTED" \
  --query 'Reservations[*].Instances[*].InstanceId'
Attack Details
Malicious Payload Capabilities
- Credential Theft: Steals NPM_TOKEN, AWS keys, GitHub tokens
- Backdoor Installation: Downloads and executes remote scripts
- Cryptomining: Installs hidden cryptocurrency miners
- Data Exfiltration: Sends environment variables to attacker servers
CI/CD Pipeline Protection
GitHub Actions Security Check
name: NPM Security Check
on: [push, pull_request]

jobs:
  security-scan:
    runs-on: ubuntu-latest
    steps:
      - uses: actions/checkout@v3
      - name: Check for malicious packages
        run: |
          if npm ls --depth=100 | grep -E 'debug@4.4.2|chalk@5.6.1'; then
            echo "::error::Malicious packages detected!"
            exit 1
          fi
      - name: Audit
        run: npm audit --audit-level=high
Prevention Checklist
- [ ] Implement package version pinning
- [ ] Enable npm audit in CI/CD pipelines
- [ ] Use private npm registry (Verdaccio/Artifactory)
- [ ] Regular dependency audits (weekly)
- [ ] Monitor package integrity hashes
- [ ] Implement least-privilege IAM policies
- [ ] Enable IMDSv2 on all EC2 instances
- [ ] Set up real-time security monitoring
Complete Package List
All 18 affected packages:
- debug@4.4.2 (357.6M downloads/week)
- ansi-styles@6.2.2 (371.41M)
- chalk@5.6.1 (299.99M)
- strip-ansi@7.1.1 (261.17M)
- ansi-regex@6.2.1 (243.64M)
- wrap-ansi@9.0.1 (197.99M)
- color-convert@3.1.1 (193.5M)
- supports-color@10.2.1 (287.1M)
- error-ex@1.3.3 (47.17M)
- color-name@2.0.1 (191.71M)
- is-arrayish@0.3.3 (73.8M)
- slice-ansi@7.1.1 (59.8M)
- chalk-template@1.1.1 (3.9M)
- supports-hyperlinks@4.1.1 (19.2M)
- has-ansi@6.0.1 (12.1M)
- simple-swizzle@0.2.3 (26.26M)
- color-string@2.1.1 (27.48M)
- backslash@0.2.1 (0.26M)
Resources & Support
- Download SSM Document: Available on GitHub repository
- NPM Security Guide: https://docs.npmjs.com/packages-and-modules/securing-your-code
- Report Issues: security@npmjs.com
Last Updated: September 10, 2025
Severity: CRITICAL
Impact: Global – All Node.js applications
Action Required: Immediate
Stay updated: Subscribe to security alerts and check back regularly for updates on this evolving situation. Report any suspicious activity to security@npmjs.com immediately.